The attack on Brevo's supply chain highlights the risks of poorly managed Cloudflare API keys
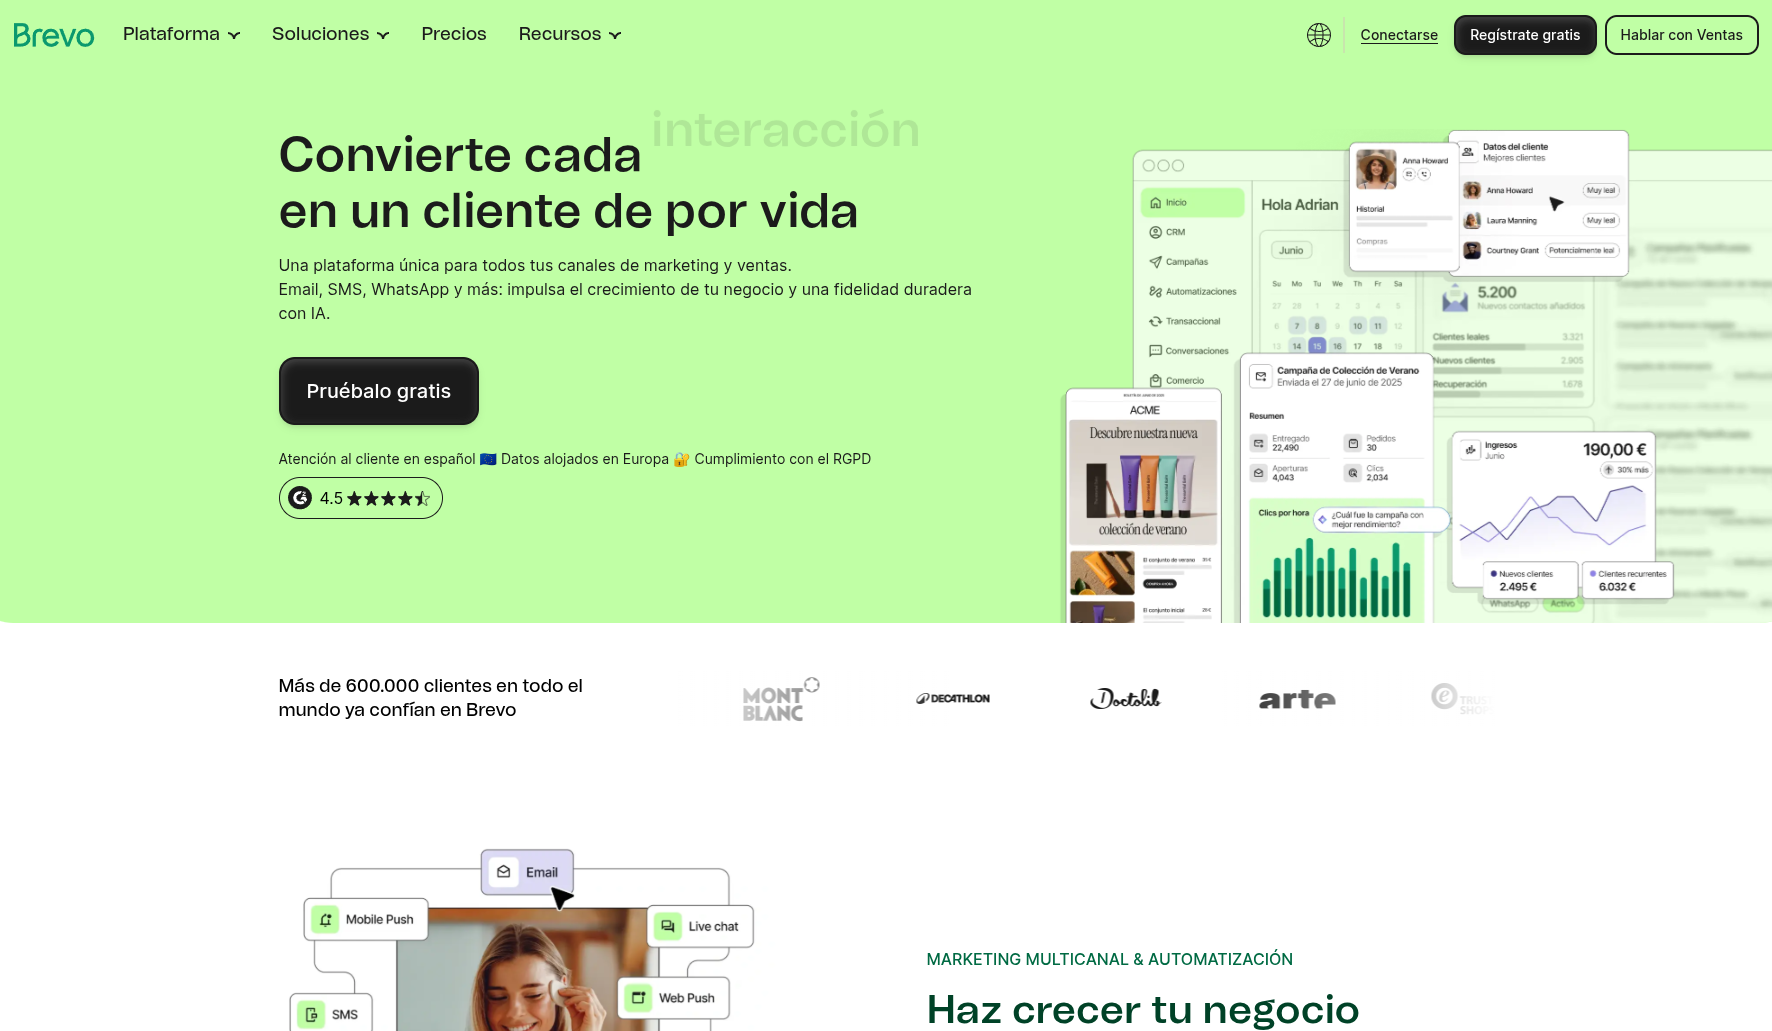
Brevo, the French email marketing platform, suffered a two-phase breach. On September 10, attackers exploited a vulnerability in its SAML SSO and gained access to 138 customer accounts. Four days later, they returned, this time using a Cloudflare API key with full permissions that had been forgotten and left embedded in the source code.
 Cloudflare
How did they do it?
Using that key, they deployed a malicious Cloudflare Worker that rewritten HTTP responses directly at the network perimeter, without touching a single source file (which made the attack very difficult to detect through traditional audits). They combined this with a hidden WordPress plugin that installed itself without requiring additional authentication in administrator sessions, and a fake “clickfix” that was only displayed to administrator accounts to evade detection systems.
Scope
More than 100,000 websites served malicious code for several hours on September 14. Among those affected are companies such as eBay, Louis Vuitton, and Michelin, and Trezor (a cryptocurrency wallet manufacturer) confirmed that 347,000 contact addresses were compromised.
Why does this matter for companies that use Cloudflare’s infrastructure?
The attack vector was not a vulnerability in Cloudflare’s own infrastructure, but rather an API credential that was never rotated. This is a stark reminder that Workers—which operate at the edge and leave no trace in the source code—are a particularly attractive target when a key is exposed. It’s time to review periodic token rotation, minimum permission scope (scoped API tokens), and audits of Worker deployments in our own accounts.